BLUE SENTINEL AI™ AI Security · AI Governance
AISPG™ governs. AegisCore AI™ operationalizes.

One AI ecosystem. One unified security and governance plane. One continuous assurance engine.

Enterprise AI now spans many clouds, models, agents, identities and security tools — but the information stays fragmented. That gap sits between AI investment and justified confidence that the environment is governed and operating within its controls. Blue Sentinel AI is developing AegisCore AI™ to close it.

We do not simply collect alerts. We aim to turn fragmented signals into traceable assurance conclusions.

View Interactive Prototype ↗

Connector qualification status.

49Contracts declared
46Registered adapters
6Pipeline-proven
0Live credential-verified

The last figure is the one that matters, so we publish it. Until it moves, no integration on this site is described as live.

Secure Posture Score · SAMPLE
0/100
Illustrative
sample data
Model Security 91
Cloud Posture 88
Governance Maturity 84
Asset Visibility 86
Remediation Velocity 79
The Doctrine Stack

Five layers. One operating system.

Each layer has one job, and each depends on the one above it.

01
AISPG™GovernsThe governing architecture — seven governance layers, eight governed AI surfaces.
02
AIGSB™Sets the standardThe AI Governance Standards Board — standards, conformance and stewardship authority. Not a government regulator.
03
AISGOS™CoordinatesThe AI Security Governance Operating System — the continuous operating model within AISPG™. How governance actually functions day to day.
04
The Assurance ChainEstablishes postureSignal → Control → Evidence → Assurance → Posture.
05
AegisCore AI™OperationalizesThe technology platform — five architecture layers running the doctrine across your estate.

AISPG™ governs. AIGSB™ sets the standard. AISGOS™ coordinates. The Assurance Chain establishes posture. AegisCore AI™ operationalizes.

The Assurance Chain

Signal → Control → Evidence → Assurance → Posture

The Assurance Chain — how raw enterprise noise becomes one number a board can act on.

01
SignalTelemetry from your existing CSPM, CNAPP, DSPM, XDR, SIEM and IAM — fused with native AI discovery.L2 · L4
02
ControlPolicy-as-code mapped to 40+ frameworks, with named ownership and governed exceptions.L3
03
EvidenceAudit-ready proof accumulating continuously from first ingestion.L3 · AISPG™ L6
04
AssuranceAdversarial testing that proves the controls actually hold. Everyone else stops at evidence.L1 · AI Security Lab
05
PostureOne Secure Posture Score, refreshed on a 60-second target cycle.L5 · Command Center

Assurance is the stage the market skips. Most platforms move signal straight to evidence and call it posture — so the score reflects what controls claim, not what they withstand.

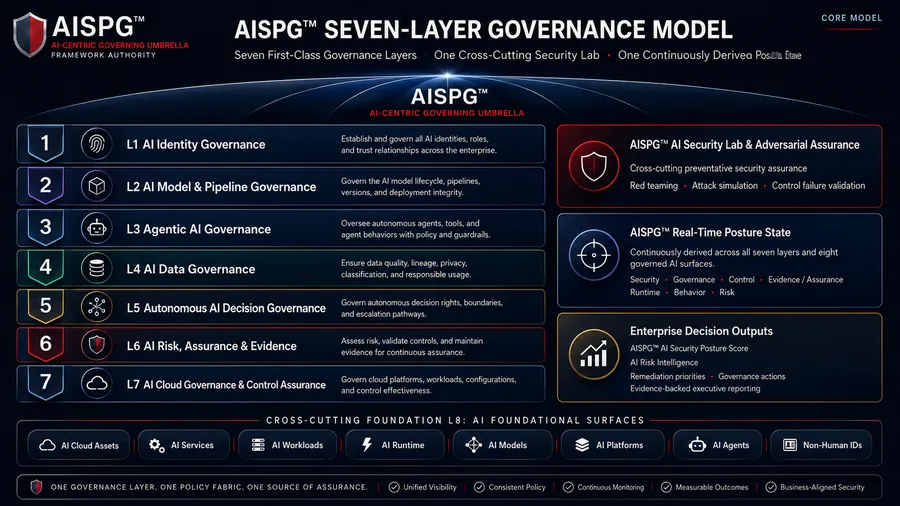
The AISPG™ Framework

The framework the platform is built on

Seven first-class governance layers, one cross-cutting AI Security Lab, and one continuously derived posture state across eight governed AI surfaces.

L1
AI Identity GovernanceAll AI identities, roles and trust relationships.
L2
AI Model & PipelineModel lifecycle, pipelines, versions, deployment integrity.
L3
Agentic AI GovernanceAutonomous agents, tools and behaviors under policy.
L4
AI Data GovernanceQuality, lineage, privacy, classification, responsible use.
L5
Autonomous AI DecisionDecision rights, boundaries and escalation pathways.
L6
AI Risk, Assurance & EvidenceRisk, control validation, continuous assurance evidence.
L7
AI Cloud GovernanceCloud platforms, workloads, configs, control effectiveness.

AISPG™ governs above and across the specialized security stack — it does not replace it. One governance layer. One policy fabric. One source of assurance.

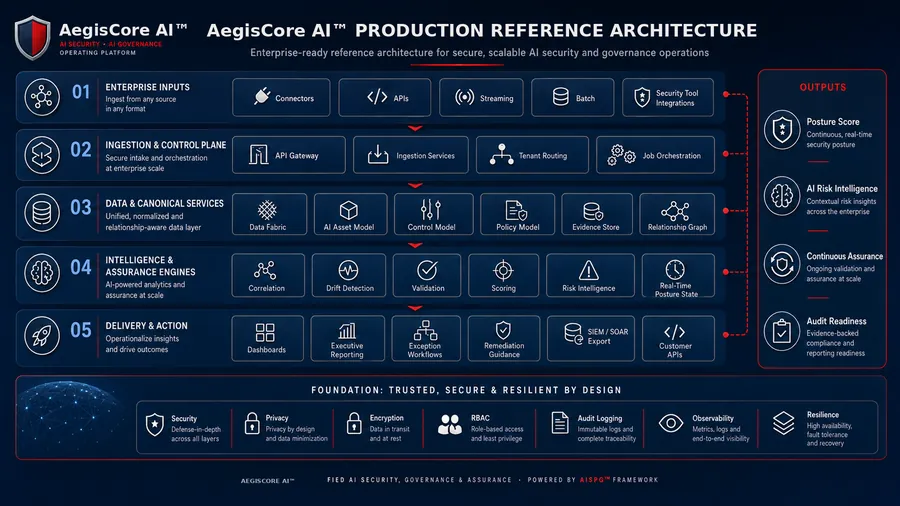
AegisCore AI™ — The Platform

Five layers. One posture score.

Tap any layer for detail.

Aggregates threat exposure, vulnerability backlog and governance control failures into one Secure Posture Score, refreshed on a 60-second target cycle. Every AI surface resolves to Governed, Degraded, Missing or Unknown.
Continuously updated inventory of every model, agent, pipeline and AI service — with behavioral baselining, drift detection, Shadow AI discovery, and non-human identity governance.
Controls mapped to 40+ regulatory frameworks. Policy-as-code enforcement. Centralized Policy Exception Management governing every waiver from request through expiration.
We don't replace your cloud stack — we integrate with it. XDR correlates telemetry from your CSPM, CWPP and CIEM tools. The Cloud Policy Plane shows what Azure, AWS and GCP actually enforce.
The strongest differentiator: continuous red teaming, adversarial testing and deception, inside an isolated sandbox with no production connectivity. Mapped to MITRE ATLAS and the OWASP LLM Top 10. Microsoft has no equivalent.
1,500+Posture checks (target)
40+Frameworks mapped
49Integration contracts
400+Playbooks (target)

Capability counts marked (target) are designed architecture targets for general availability, not verified live coverage.

Visual Doctrine Library

The architecture, drawn

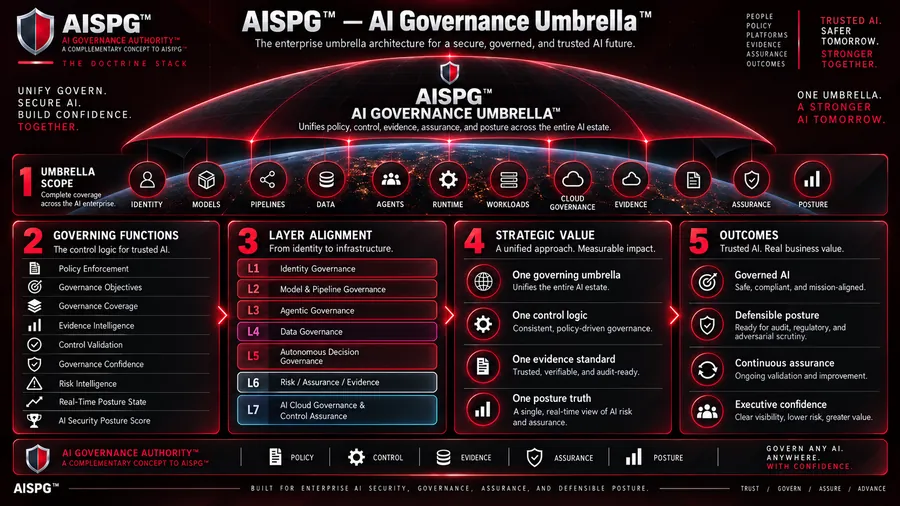
AISPG™ — AI Governance Umbrella™
AISPG™ — AI Governance Umbrella™Flagship
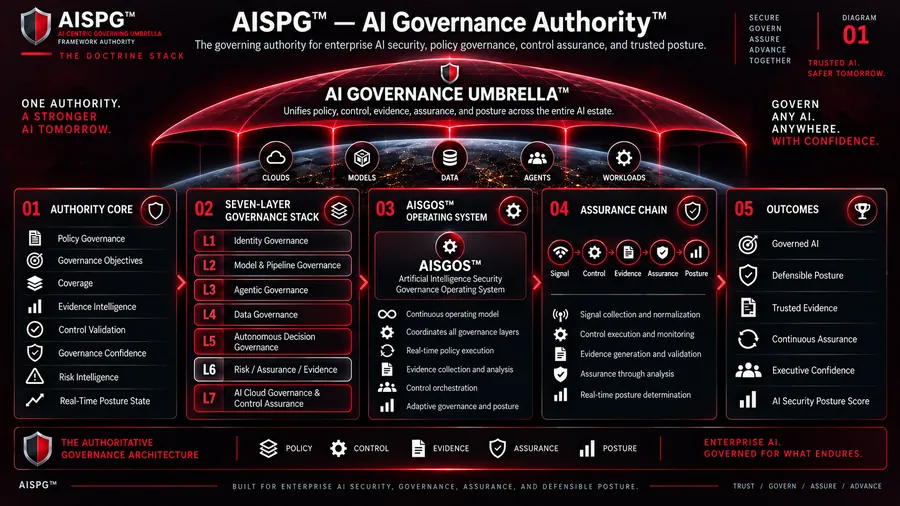
AISPG™ — AI Governance Authority™
AISPG™ — AI Governance Authority™Framework
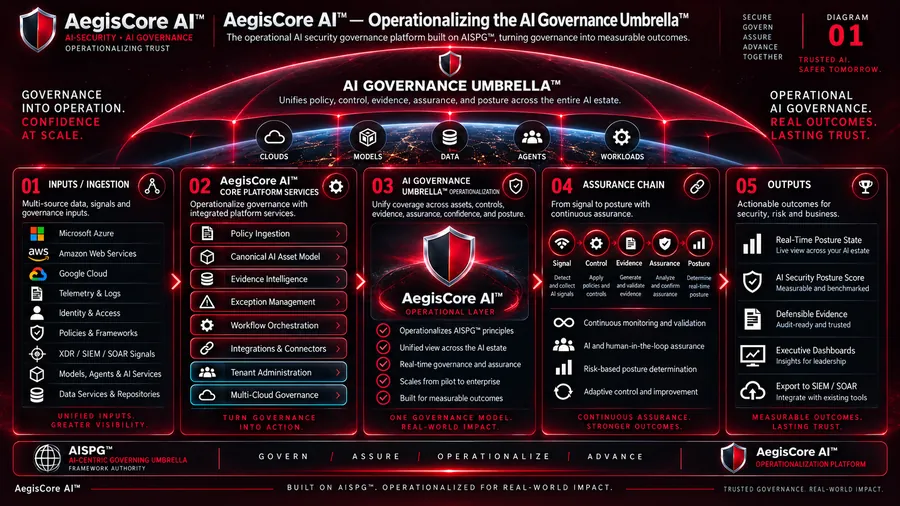
AegisCore AI™ — Operationalizing the AI Governance Umbrella™
AegisCore AI™ — Operationalizing the AI Governance Umbrella™Platform
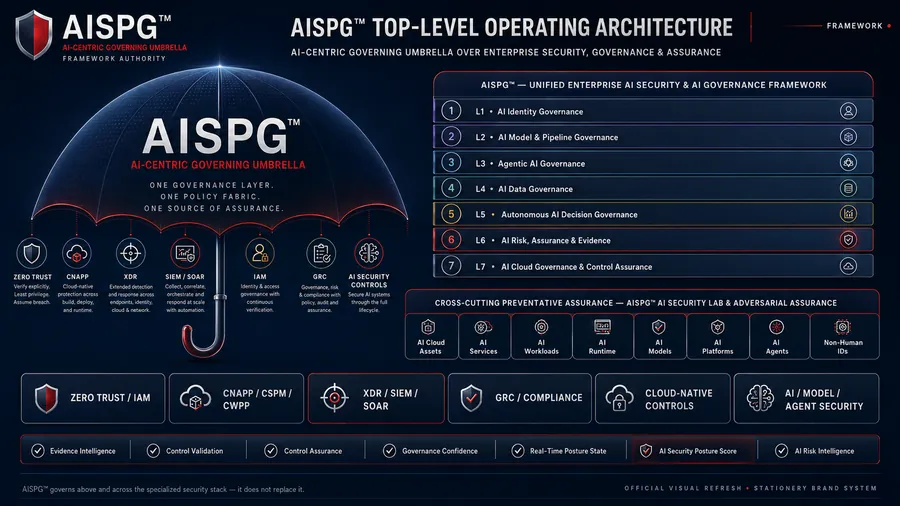
AISPG™ Top-Level Operating Architecture
AISPG™ Top-Level Operating ArchitectureFramework
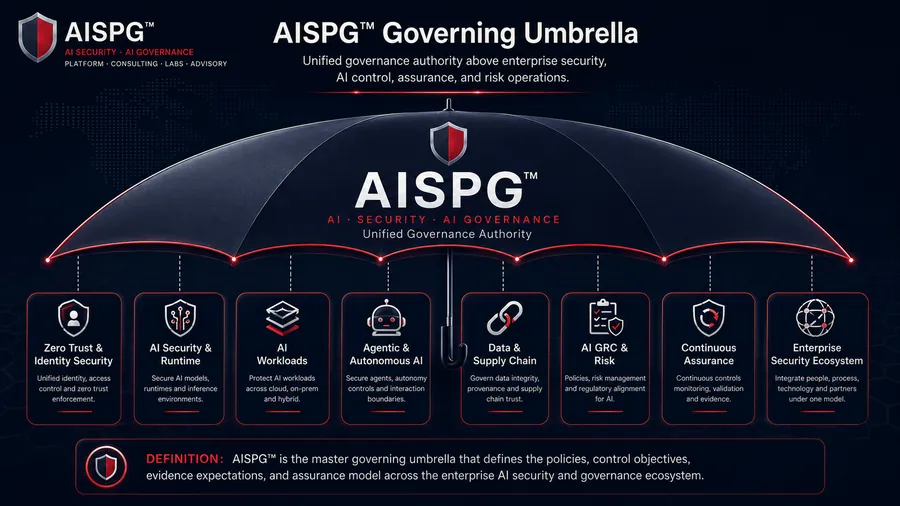
AISPG™ Governing Umbrella
AISPG™ Governing UmbrellaFramework
AISPG™ Seven-Layer Governance Model
AISPG™ Seven-Layer Governance ModelFramework
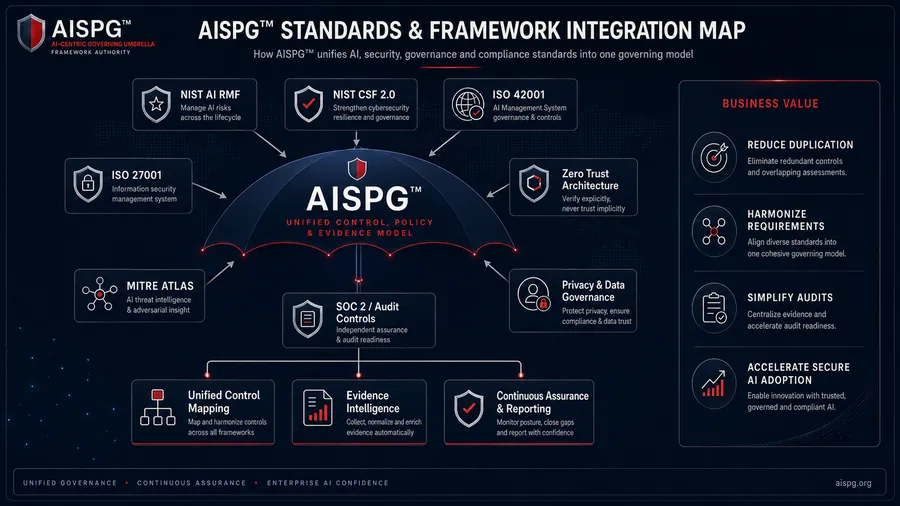
AISPG™ Standards & Framework Integration Map
AISPG™ Standards & Framework Integration MapFramework
AegisCore AI™ Production Reference Architecture
AegisCore AI™ Production Reference ArchitecturePlatform
← Swipe to browse · 12 diagrams
Start Here

The Enterprise Proof of Value

On your environment, against your own models. Scoped & qualified, with conversion pricing and the decision date agreed up front — so there's nothing to negotiate at the end.

WK 1–2
Discovery & BaselineInventory every model, agent, pipeline and non-human identity — including the shadow AI nobody registered.
WK 2–4
The Lab Tests Your ModelsAdversarial testing inside an isolated sandbox. Never touches production.
WK 5
Executive ReadoutBoard-ready findings, framework coverage, and a modelled dollar-exposure range.
DAY 60
Your DecisionDecide with your own data in front of you — not a vendor projection.
Scoped & qualifiedPricing agreed up front Your environmentZero production connectivity

White papers

Read the opening pages free. The complete PDF is available once you tell us who you are.
Trust Center

We hold ourselves to the standard we sell

You're evaluating a security company. Our own posture is part of your diligence. We publish status honestly — including what's still in progress.

SOC 2 Type IIIn progress
ISO/IEC 27001In progress
ISO/IEC 42001In progress
FedRAMP ModeratePlanned
DoD IL4 / IL5Planned
GDPR / CCPAOperating
Straight Answers

Questions buyers actually ask

Keep them. Cloud security stops at infrastructure — models, agents, NHIs, MCP endpoints and model artifacts sit outside a CNAPP graph entirely. We correlate their telemetry and add the layers none of them cover. Additive, not rip-and-replace.
Discovery usually says otherwise. Shadow AI and orphaned service identities accumulate between reviews. Governance is far cheaper to establish before scale than after.
A policy without enforcement and evidence is a document. L3 maps each policy to your frameworks with control ownership and audit-ready evidence.
A team can build a dashboard. It cannot replicate an adversarial testing lab, the designed target of 1,500+ posture checks, and 40+ framework mappings — and keep all of them current.
A Proof of Value is scoped to your environment, and the Breach Impact Modeler produces a dollar-exposure range from your own baseline. Most customers fund the platform from the point tools it consolidates.
Evidence & Verification

What is evidenced — and what is still being built

Every capability claim is classified against the evidence behind it.

01
QUALIFIED_LIVENot yet claimedVerified operating against a real external system with real credentials, under qualification conditions. Not yet claimed for any connector.
02
DEMONSTRATED_SANDBOXEngineering-verifiedExecuted and evidenced inside a controlled engineering environment, without live customer data. Development line v2.7.0-qc29 over the independently reviewed v2.5.5 baseline. “Production ready” is explicitly not claimed by that baseline.
03
INTERACTIVE_FIXTURESynthetic dataA working interface driven by synthetic, deterministic sample data. The prototype, posture gauges and sample scores on this site.
04
ARCHITECTURE_TARGETDesigned, not shippedThe intended end state, not shipped inventory. Integration, posture-check and remediation-playbook counts.
05
PLANNED_ROADMAPCommitted directionA named target, not yet built. Published on the AISPG™ roadmap with dates.
06
UNVERIFIEDNot usedAsserted but not independently substantiated. Nothing on this site carries this label; where it would, the claim was removed instead.

Pre-general-availability. AegisCore AI™ is in development. We do not claim general availability, production certification, live customer deployments or qualified live connectors. No certifications or government hosting authorizations are held; framework names denote control-mapping targets.

Missing evidence is never treated as a pass. The Assurance Chain exists so that an absent control, a stale artefact or an unobserved asset resolves to MISSING or UNKNOWN — never to a silent pass.

AIGSB™ is a concept, not a board. AIGSB™ is a designed governance concept, not an operating body. No examinations are administered, no credentials are issued, and no conformance assessments are performed under this concept today. It carries no governmental or regulatory authority. AISPG™, AISGOS™ and AIGSB™ are marks of the Founder, licensed to Blue Sentinel AI, Inc.